With either a local LLM or a high-performance external LLM, AI automatically analyzes infrastructure and executes automatic attack defense in production. Bandwidth quality is in staged deployment, moving from observation to dynamic control.
Dual-axis security and quality modules address operational challenges.
Delivering “AI Ops” in areas
where cloud AI cannot reach, in closed networks or with external LLMs
Cloud-based agentic AI such as AWS DevOps Agent and Azure Security Copilot is powerful, but it cannot reach closed-network environments, on-premises physical equipment, and “operational challenges beyond security.”
Data Sovereignty Issues
Logs are sent to cloud vendor AI platforms. Cannot be used in closed-network environments for financial institutions, government agencies, and healthcare.
Opacity of Usage-Based Pricing
AWS DevOps Agent charges $0.0083/second on a usage basis. Costs balloon as investigation frequency increases, making budgets unpredictable.
Operational Challenges Extend Beyond Security
Beyond attack detection, there are many operational challenges to entrust to AI: bandwidth quality, resource optimization, cost management, and more.
A platform where two modules
operate in parallel
BASTION is not a single-function product but an AI Ops Platform providing multiple modules. Each module has an independent failure boundary, so one module’s failure does not cascade to another.
Security Module
From attack detection to automatic defense. A multi-layer correlation engine combines detections from individual devices and visualizes entire attack campaigns. Executes simultaneous defense across multiple systems within 8 seconds of detection.
- Multi-layer correlation engine (FW/VPN/authentication/application/endpoint)
- Coordinated attack group detection (same subnet and ASN units)
- Cascade defense (boundary device + DMZ Agent simultaneous blocking)
- Lightweight Agent for DMZ and isolated environments
Quality Module
Continuous observation of bandwidth usage and dynamic allocation control. Accurate aggregation using virtual platform network identifiers directly, time-based threshold judgment, and weighted allocation implemented. Production deployment proceeds in stages.
- VM traffic collection at regular intervals
- Threshold judgment by subnet, time zone, and direction
- Dynamic rate control with weighted allocation during congestion
- Dry-run mode for observation → staged deployment
Operational Self-Healing and Self-Evolution
A third direction beyond monitoring and defense: the platform will self-heal its own operations and continuously self-improve its detection logic. All changes inherit the “AI proposes, humans approve” safety gate.
- Operational self-healing (automatic detection of pipeline anomalies and recovery proposals)
- Autonomous updating of detection logic (continuously learns attack trends and proposes new rules; applying them requires human approval)
- Automatic ticket creation via external API integration (Jira / Redmine, etc.)
- Management Console integrated visualization
- Resource optimization recommendations
Simple configuration, powerful automation
Composed entirely of open source. In a closed-network configuration, it operates entirely within the customer network and sends no log data externally. Configurations that leverage external LLMs can also be selected according to requirements.
Local LLM (Qwen2.5-14B), rsyslog, shell scripts, SQLite. In a closed-network configuration, no internet connection is required.
Actually running on our own infrastructure
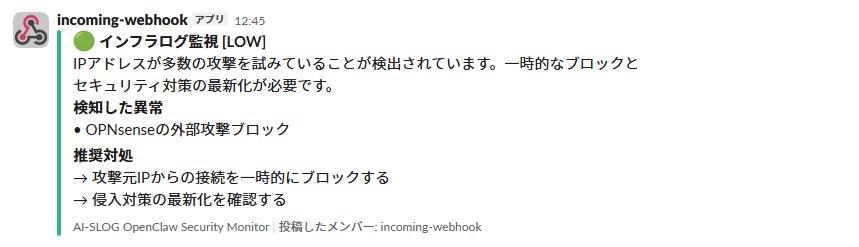
BASTION operates 24/7 in BESTNET-CLOUD’s production environment. The security module protects 10 devices, and the quality module observes 76 virtual machines.
Automatic cascade defense activation
SECURITY
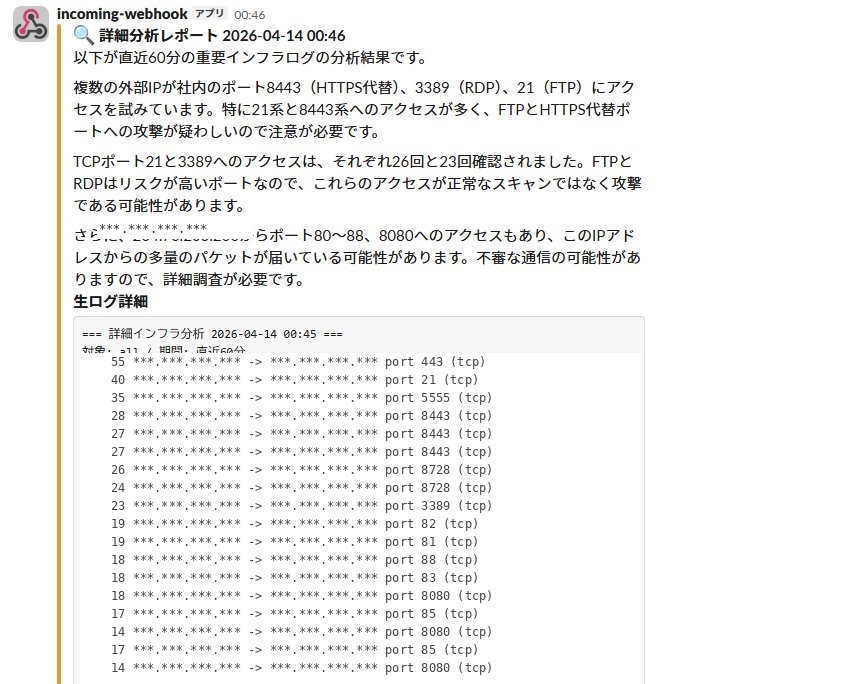
Automatic daily report
OPS
“Do not rely entirely on AI”
Operational safety design
When introducing automatic control to production infrastructure, handling AI judgment errors and unforeseen situations is essential. BASTION builds human approval gates into an agentic workflow in which AI agents handle observation, analysis, and implementation, and adopts a staged design that clearly separates “human judgment” from “AI implementation.”
Stage A — Current status assessment by AI
AI performs read-only investigation and reporting. Does not output judgment or evaluation. Zero impact to production.
Stage B — Judgment by operators
All judgments—classification, threshold setting, production mode switching—are made by operators. Not delegated to AI.
Stage C — Implementation by AI
AI implements accurately based on operator judgment. Production writes follow “dry-run → limited production → full production” in three stages. Emergency stop command always ready.
Basic principles of AI cooperation
VM classification, network configuration, data structure details, and organization-specific context. These are factual domains only operators understand. BASTION is designed so AI “does not guess but asks for confirmation.” We have systematized 10+ lessons learned in actual operations as “design principles” and reflected them in all new implementations.
Differences from existing solutions
BASTION does not ask whether a single metric has crossed a threshold; it captures whether multiple observation surfaces have begun to break down in lockstep (coordinated onset), using relative change from each target’s own baseline. It detects coordinated patterns that thresholds, absolute values, and global SIEM miss.
| Cloud AI monitoring (AWS/Azure) | Traditional SIEM/SOAR | BASTION | |
|---|---|---|---|
| Data sovereignty | External transmission | Product dependent | Selectable from closed-network to hybrid |
| Billing model | Usage-based | License | Scope-based estimate |
| Attack campaign detection | ○ | Fixed rules | Mathematical judgment + coordinated attack grouping |
| DMZ and isolated environment support | × | Limited | Dedicated Agent + verification engine |
| Dynamic bandwidth quality control | × | × | ○ (Quality module, in staged deployment) |
| Production deployment safety | Vendor dependent | Fixed behavior | Three-stage mode + emergency stop |
| Adding devices | API integration required | Custom implementation | Syslog connection only |
“Mathematical judgment” is a proprietary model that combines an evaluation of traces penetrating non-adjacent defense layers in temporal alignment (cross-layer correlation) with a relative evaluation against each target’s own baseline, based on independent research by Hideyuki Chinda (representative). Details (formulas and parameters) are non-public because a patent application has been filed (2026), but conceptual level details are gradually disclosed in our tech blog.
Watch the coordination of change, not the value
It is not about whether a single metric crossed a threshold. Each defense layer deviates relative to its own baseline and rises together within the same time window — this coordinated onset (co-onset) is what the multi-layer correlation engine captures. Isolated spikes are ignored.
A “coordinated pattern” is flagged only when multiple defense layers rise together within the same time window. Each layer is judged by its relative change from its own baseline, and isolated spikes (unrelated fluctuations) are ignored. What the multi-layer correlation engine captures is the cross-layer coordination that global thresholds or absolute values cannot see.
Security and quality capabilities on two axes
🛡 Security Module
- Multi-layer correlation campaign detection — Cross-layer analysis of 5 layers. Visualizes attack scenarios invisible to individual devices
- Coordinated attack group detection — Unified grasp of organized attacks at same subnet and ASN units
- Cascade defense — Single detection propagates to multiple devices simultaneously. Simultaneous boundary device + DMZ Agent blocking
- OS-unified blocking method — Unified to firewalld/ufw/iptables. Does not depend on customer environment middleware
- DMZ dedicated Agent — WebSocket communication. Agent side minimal privilege with dual-layer protection by verification engine
- Automatic device classification — Monitoring begins by directing syslog. Zero registration work
- Whitelist protection — Physically prevents accidental blocking of company IPs and partner IPs
- 24-hour automatic release — Even temporary false positives do not result in permanent blocking
📊 Quality Module
- Accurate aggregation based on virtual platform identifiers — VM identification obtained directly from virtual platform network identifiers, eliminating false positives
- Judgment by subnet, time zone, and direction — Individual threshold design matched to line characteristics
- Dynamic rate control — VM-level control with weighted allocation during congestion
- Weight control — Operators can adjust VM-level priority at their discretion
- Dry-run default — Operates for observation only; production mode switching is operator decision
- Staged production deployment — Careful rollout from single subnet limitation to all subnets
- Emergency stop command — Immediate release of all control implemented from the start
- Automatic release — Automatically releases control after 15 continuous minutes of congestion resolution
Harness-based
hybrid LLM integration
Based on local LLM (Qwen2.5-14B), BASTION also integrates with high-performance external LLM APIs such as Claude and GPT. Through a harness that appropriately selects LLMs by use case, we can address both routine task automation and unexpected issues.
Routine task automation
Automate periodic reports, inventory, and operational record organization—routine tasks where external LLMs excel. Delegate transcription and structuring while keeping judgment with humans.
Advanced reasoning during problem occurrence
In complex problems not encountered during normal operations or unexpected failure scenarios difficult for local LLMs, leverage external LLM reasoning power.
Harness-based switching control
A harness controls which LLM to use in which scenario. Cost, data sovereignty, and reasoning performance balance can be designed per customer environment.
Technical details publicly available
We believe “whether it can be operated” is the ultimate differentiator and actively disclose design decisions and operational know-how at the conceptual level. Specific customer IP, organizational information, and patent-related formulas remain confidential.
The more beautiful the design, the more we doubt it with real data — verification discipline
Before putting automated control into production, we refute our own hypotheses with real data — BASTION’s verification discipline.
Read article →Automatic infrastructure log analysis with local LLM
Implementation record of local LLM (Qwen2.5-14B + GPUStack) achieving both accuracy and determinism in log analysis.
Read article →How multi-layer correlation campaign detection works
Design that visualizes attack scenarios invisible in single-device logs through cross-layer tracing.
Read article →Lightweight Agent for DMZ and verification engine
Design that “does not trust Agents” in DMZ environments where compromise is possible.
Read article →LLM hallucination audit implementation
A mechanism that automatically cross-references fake incidents created by AI against actual machine logs.
Read article →Start with a consultation
We conduct interviews on target devices and requirements, then provide proposals based on scope.
You can deploy either the security module alone or both modules together.
Revision History
| Date | Version | Changes |
|---|---|---|
| 2026-04-16 | v1.0 | Initial release. Architecture diagram, 5 Slack screenshots, competitor comparison table, feature list. |
| 2026-04-17 | v1.1 | Added cross-layer analysis (OPNsense × AD) screenshot to Evidence section. Added HP navigation. |
| 2026-04-21 | v2.0 | Added automatic device classification and endpoint monitoring to feature list. Added tech blog section with 4 posts. |
| 2026-04-23 | v2.1 | Added reactive defense (automatic attack source IP blocking, fully automated operation). |
| 2026-04-24 | v2.2 | Added multi-layer correlation campaign detection. Updated to 8 tech blog posts. |
| 2026-05-10 | v2.3 | Redefined BASTION as AI Ops Platform. Changed to dual-axis structure: security module + quality module. Reflected coordinated attack group detection, cascade defense, DMZ Agent, and AI cooperation safety design (stages A/B/C, dry-run default). Incorporated figures: 10 security defense devices, 76 quality module observation VMs. Added hybrid LLM integration by harness (experimental stage) section. |
| 2026-05-14 | v2.4 | Published 3 tech blog articles (multi-layer correlation campaign detection / DMZ Agent and verification engine / local LLM infrastructure log analysis). Updated related links in LP to actual URLs. Added NEW and Coming soon badges. |
| 2026-06-09 | v2.5 | Updated the patent application status from “in preparation” to “filed (2026).” Clarified the quality module’s operational status as “in staged deployment” in the hero section and comparison table (security = executed in production / quality = staged deployment from observation). |
| 2026-06-12 | v2.6 | Published “The more beautiful the design, the more we doubt it with real data (BASTION verification discipline)” on the tech blog. Added an article card to the TECH BLOG section. |
| 2026-06-13 | v2.7 | Converted the tech blog section into cards (with the highlighted article “verification discipline” shown as a featured card). Rolled out the verification discipline article and the multi-layer correlation engine visualization to 5 languages. |
| 2026-10-17 | v2.8 | Removed the “experimental stage” label from external LLM integration in the EXTENSIBILITY section. |